

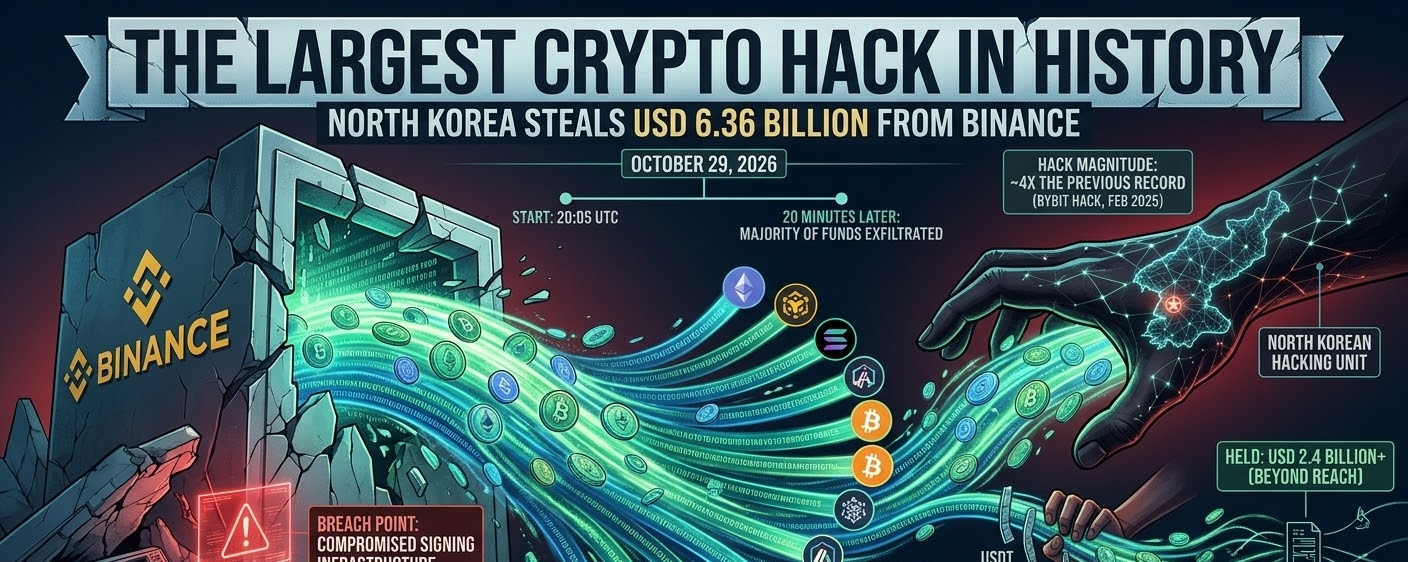
In what has officially been categorized as the largest cryptocurrency theft in history, approximately USD 6.36 billion was drained from Binance wallets across ten different blockchains. The overwhelming majority of the funds were siphoned away in a chillingly fast 20-minute window beginning at 20:05 UTC.
Leading blockchain intelligence and cybersecurity firms, including TRM Labs and Elliptic, have attributed the massive operation with high confidence to TraderTraitor (also widely tracked as part of the state-sponsored Lazarus Group), an elite hacking unit tied to North Korea.
Anatomy of the Heist: How the Attack Unfolded
The staggering scale of the breach makes it roughly four times larger than the previous record-holder—the USD 1.5 billion hack on Bybit in February 2025.
The Timeline: Starting sharply at 20:05 UTC, attackers targeted Binance wallets spanning ten distinct blockchains, moving billions in a matter of minutes. The first wave hit the XRP Ledger, followed swiftly by rapid outflows across Solana, Ethereum, Optimism, Arbitrum, and others.
The Infrastructure Compromise: Rather than breaking the core cryptography, investigators noted that the attack bore similarities to earlier state-backed heists—pointing to a deep compromise of signing infrastructure. On Ethereum, the attacker leveraged pre-signed authorizations and smart contract delegations to turn a Binance hot wallet into an attacker-controlled sweeper.
The Scale: Four primary assets—USDT on Ethereum, Bitcoin (BTC), USDC, and USDT on Tron—accounted for nearly 74% of the total stolen volume.
A High-Stakes Race: Freezes and Counter-Measures
As soon as the breach was detected, a massive coordinated effort swung into action across the crypto ecosystem to stymie the hackers.
The Freezes: Major token issuers and protocol security councils—including Tether, Circle, Ripple, World Liberty Financial, and Arbitrum—rapidly blacklisted addresses and froze assets. Roughly USD 2.7 billion in stablecoins and network tokens were successfully frozen.
The Attacker's Counter-Moves: To outpace the incoming freezes, the attackers aggressively swapped tokens, sold USDT to market makers, and even borrowed ETH against collateral on decentralized finance (DeFi) protocols like Aave.
Current Status: Despite billions being locked down by swift industry coordination, the bad actors still retained over USD 2.4 billion in unfreezeable assets—such as massive holdings of Bitcoin and Ethereum—beyond the reach of any single issuer.
Growing State-Sponsored Cyber Threats
This historic incident dramatically underscores the growing sophistication of North Korean state-sponsored cyber operations. According to on-chain tracking data, this single heist nearly doubles the total cumulative volume of cryptoassets previously attributed to North Korean state actors over the years.
While Binance quickly suspended withdrawals on affected networks and assured users that customer funds remained safe, the attack serves as a stark reminder of the monumental security challenges facing centralized exchange infrastructure and cross-chain asset management. As blockchain investigators continue tracking the automated layering scripts and cross-chain mixing of the remaining funds, the event will likely trigger a massive overhaul of institutional hot wallet governance industry-wide.#BinanceSAFUFundTransferCompleted7499BTC #BinanceRecovery90% of stolen assets #CZSaysCompensationIsinPlaceUsersAreProtected #YiHe:ProofOfReserves:10TokensAt100%Backing #CZSaysCompensationIsinPlaceUsersAreProtected #BackedNotBroken:RichardTengSaysUsersBearNoLoss