CRITICAL SECURITY ALERT: Crypto Tech Provider Haruko Hit by Cyberattack, 15 Institutional Clients Affected
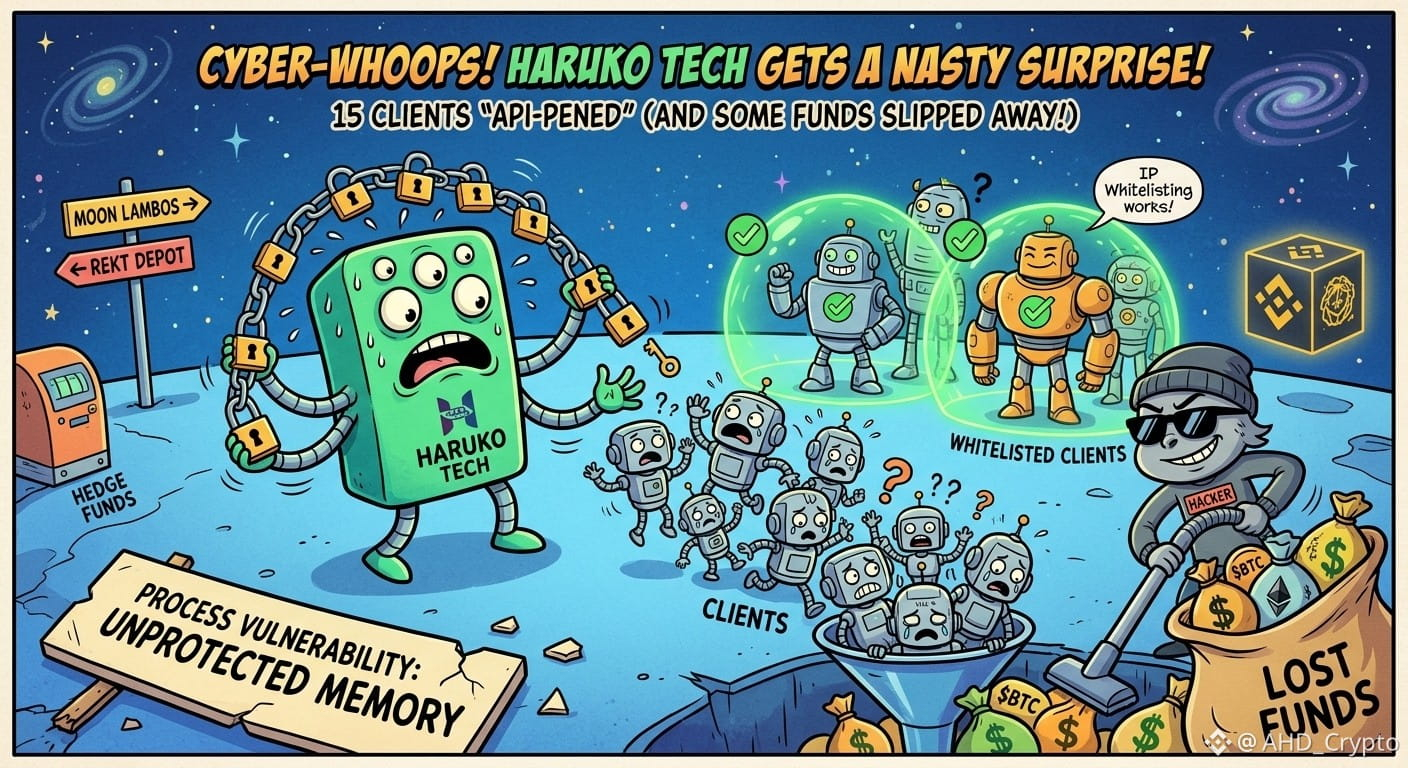
Crypto technology infrastructure provider Haruko has suffered a targeted cyberattack, exposing read-only exchange API credentials and trading data across 15 non-whitelisted institutional clients. Sources familiar with the breach report that a small amount of funds was stolen, particularly impacting smaller hedge funds with weaker security controls.
🔑 Key Takeaways & Attack Mechanics
>> Root Cause: Attackers exploited a process-level vulnerability in Haruko’s bare-metal server setup to extract user access tokens directly from memory.
>> Impacted Data: Read-only exchange API keys and active trading data were compromised. Client account credentials were NOT directly leaked.
>> Losses: While API keys were read-only, secondary vulnerabilities or weaker internal operational controls allowed bad actors to steal funds from select institutional accounts.
>> Remediation: Haruko has patched the vulnerability, rotated server-side secrets, and strongly advised all clients to enforce IP whitelisting immediately.
💡 Why Security Hygiene Matters for Every Trader
Third-party API breaches are a prime vector for institutional and retail compromises alike. Protect your assets on $BTC , $ETH ,$BNB , and beyond by strictly applying basic operational security:
1- Enable IP Whitelisting: Restrict API access exclusively to trusted, static IP addresses.
2- Disable Withdrawal Permissions: Never enable withdrawal rights on third-party integration API keys unless absolutely necessary.
3- Regular Key Audits: Periodically delete and regenerate older, unused API connections.
#writetoearn #BTC #ETH #bnb #CryptoSecurity
Crypto technology infrastructure provider Haruko has suffered a targeted cyberattack, exposing read-only exchange API credentials and trading data across 15 non-whitelisted institutional clients. Sources familiar with the breach report that a small amount of funds was stolen, particularly impacting smaller hedge funds with weaker security controls.
🔑 Key Takeaways & Attack Mechanics
>> Root Cause: Attackers exploited a process-level vulnerability in Haruko’s bare-metal server setup to extract user access tokens directly from memory.
>> Impacted Data: Read-only exchange API keys and active trading data were compromised. Client account credentials were NOT directly leaked.
>> Losses: While API keys were read-only, secondary vulnerabilities or weaker internal operational controls allowed bad actors to steal funds from select institutional accounts.
>> Remediation: Haruko has patched the vulnerability, rotated server-side secrets, and strongly advised all clients to enforce IP whitelisting immediately.
💡 Why Security Hygiene Matters for Every Trader
Third-party API breaches are a prime vector for institutional and retail compromises alike. Protect your assets on $BTC , $ETH ,$BNB , and beyond by strictly applying basic operational security:
1- Enable IP Whitelisting: Restrict API access exclusively to trusted, static IP addresses.
2- Disable Withdrawal Permissions: Never enable withdrawal rights on third-party integration API keys unless absolutely necessary.
3- Regular Key Audits: Periodically delete and regenerate older, unused API connections.
#writetoearn #BTC #ETH #bnb #CryptoSecurity