⚠️ $MINIMA Web Wallet Security Incident ⚠️
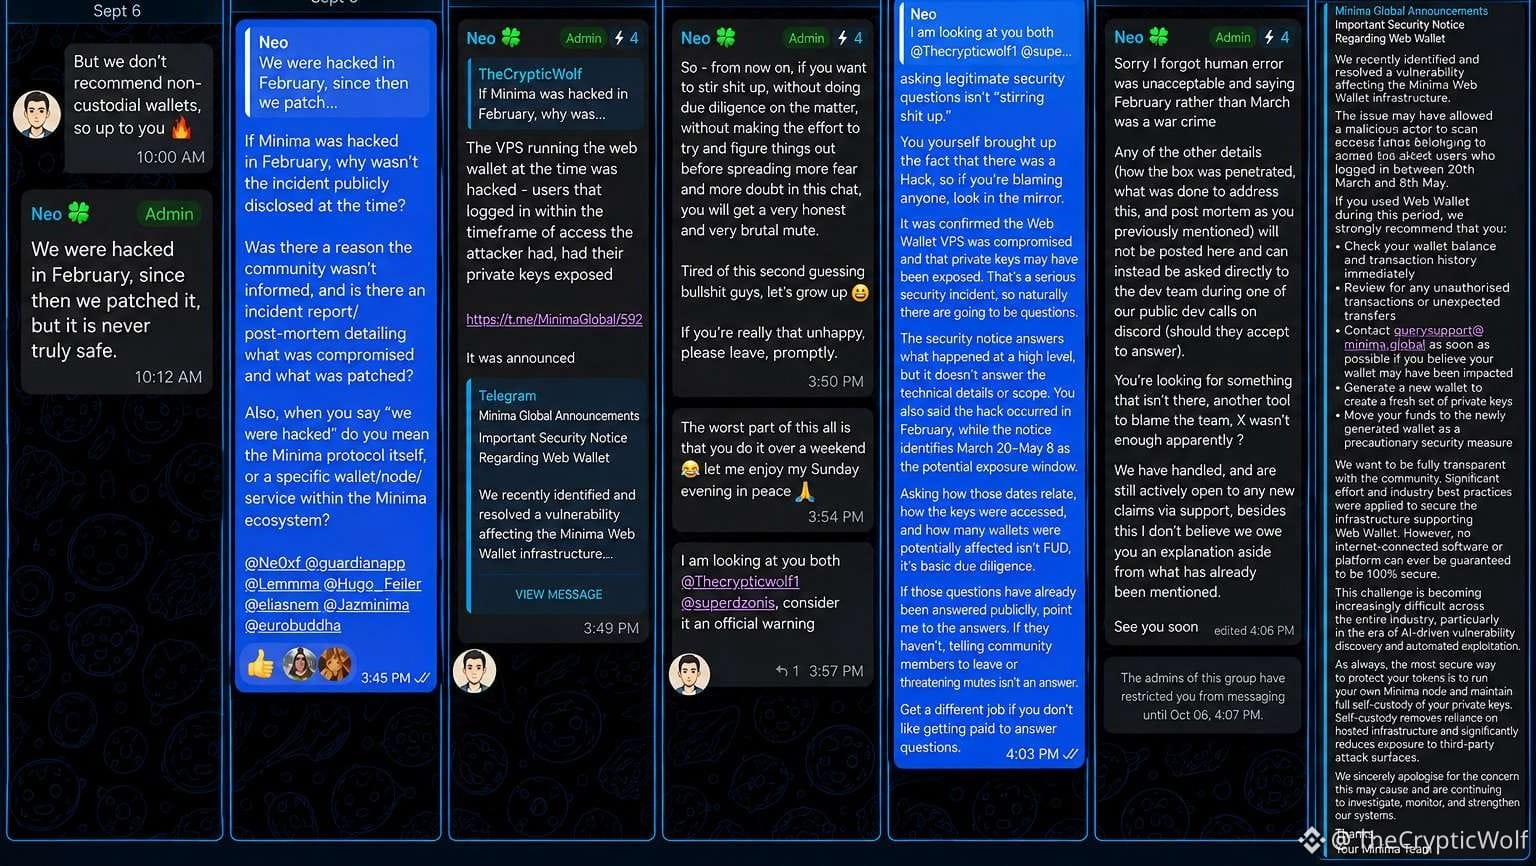
According to Minima's own security notice, a vulnerability may have allowed a malicious actor to scan exposed private keys and access funds belonging to some web wallet users who logged in between March 20th and May 8th. Users were advised to generate new wallets and move their funds.
In Telegram, Minima's Products & Community Ops Lead also stated today: "We were hacked in February"
He later clarified that the VPS running the web wallet was compromised and that users who logged in during the attacker's access period had their private keys exposed.
I asked:
-How were private keys technically exposed?
-How many wallets were potentially affected?
-How does the February compromise date relate to the March 20th-May 8th exposure window?
-Was there an incident report/post-mortem detailing what happened and what remediated?
I was subsequently issued an "official warning" and ultimately banned from the Minima TG group until October 6th.
I was later told after the ban, the February date was human error, and that the additional technical questions could be directed to the development team during a discord forum "should they accept to answer."
One other point worth noting:
I have NOT found an official security disclosure about this incident on @Minima_Global main X account.
However it was disclosed on May 21st, nearly two weeks after the fact in the Minima official TG announcement channel.
I'm not claiming the Minima blockchain itself was hacked. The disclosed incident concerns the web wallet infrastructure, which is extremely serious, considering private keys were exposed and funds were potentially stolen.
I'm simply documenting what Minima disclosed, what remains unanswered publicly, and what happened when those questions were asked.
Security incidents deserve transparency. Asking questions about the scope, timeline, attack mechanism, and remediation is basic due diligence, not FUD.
According to Minima's own security notice, a vulnerability may have allowed a malicious actor to scan exposed private keys and access funds belonging to some web wallet users who logged in between March 20th and May 8th. Users were advised to generate new wallets and move their funds.
In Telegram, Minima's Products & Community Ops Lead also stated today: "We were hacked in February"
He later clarified that the VPS running the web wallet was compromised and that users who logged in during the attacker's access period had their private keys exposed.
I asked:
-How were private keys technically exposed?
-How many wallets were potentially affected?
-How does the February compromise date relate to the March 20th-May 8th exposure window?
-Was there an incident report/post-mortem detailing what happened and what remediated?
I was subsequently issued an "official warning" and ultimately banned from the Minima TG group until October 6th.
I was later told after the ban, the February date was human error, and that the additional technical questions could be directed to the development team during a discord forum "should they accept to answer."
One other point worth noting:
I have NOT found an official security disclosure about this incident on @Minima_Global main X account.
However it was disclosed on May 21st, nearly two weeks after the fact in the Minima official TG announcement channel.
I'm not claiming the Minima blockchain itself was hacked. The disclosed incident concerns the web wallet infrastructure, which is extremely serious, considering private keys were exposed and funds were potentially stolen.
I'm simply documenting what Minima disclosed, what remains unanswered publicly, and what happened when those questions were asked.
Security incidents deserve transparency. Asking questions about the scope, timeline, attack mechanism, and remediation is basic due diligence, not FUD.